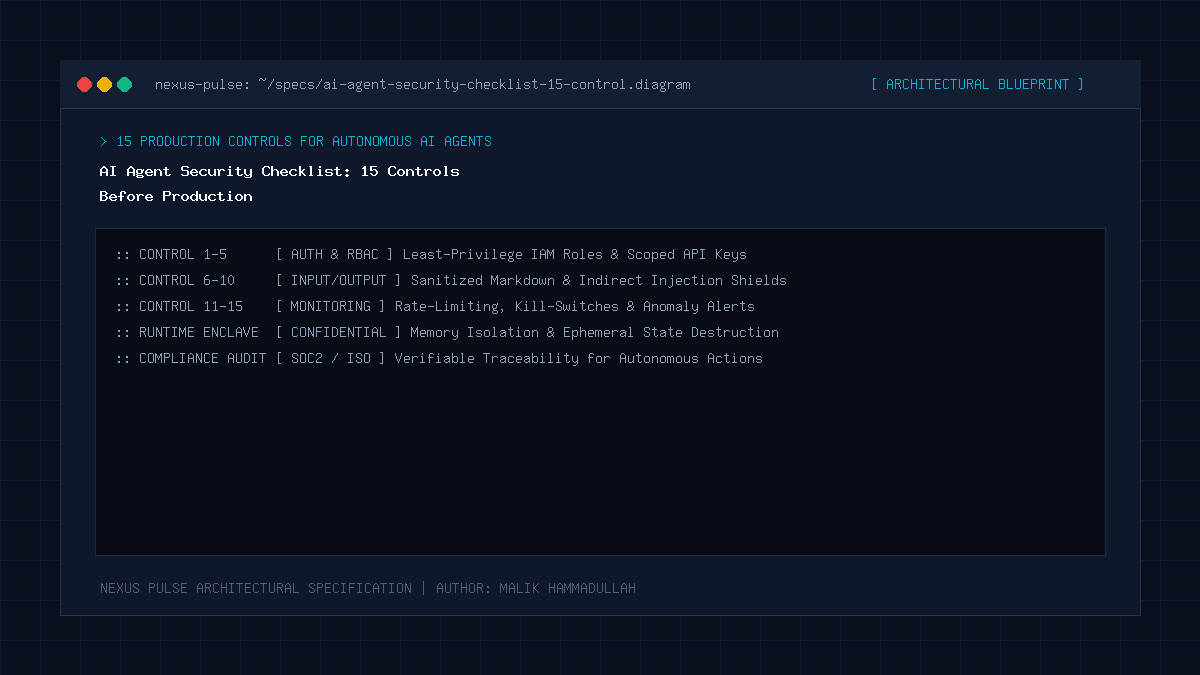
The 15 controls require isolating tool execution inside ephemeral containers, enforcing strict schema parsing, restricting outbound network egress, establishing human-in-the-loop approval gates, and running automated adversarial red-team benchmarks prior to production release.
Key Takeaways & Quick Summary
- Autonomous agents require defense-in-depth isolation across input, execution, network, and storage layers.
- Never grant agents direct access to raw bash or SQL interpreters without parameter sanitization middleware.
- Outbound network egress must be blocked by default to prevent silent exfiltration of customer data and API keys.
- Automated red teaming should simulate indirect prompt injection and memory poisoning continuously in CI/CD.
The High Cost of Unchecked Autonomy
Deploying an autonomous AI agent into production without rigorous security controls is the operational equivalent of granting an anonymous contractor root SSH access to your production database. While agentic workflows unlock unprecedented automation, they introduce unprecedented attack surfaces.
In 2026, automated threat actors deploy specialized autonomous scanners that identify agentic endpoints, probe for indirect prompt injection vulnerabilities, and exploit unvalidated function calls to pivot deeper into corporate cloud infrastructure.
This 15-point checklist serves as the definitive enterprise standard for securing agentic software architectures prior to public production release.
Layer 1: Input & Prompt Boundary Isolation
Control 1: Implement Token-Level Data Delimitation using custom cryptographic XML tags. Control 2: Deploy a Dual-LLM Quarantine pattern for all unstructured external documents. Control 3: Enforce strict character set filtering and length quotas on inbound prompt payloads.
Control 4: Strip executable script tags and macro payloads from uploaded binary files (PDFs, DOCX, XLSX) before text extraction passes.
Control 5: Maintain immutable system prompts that cannot be modified by downstream agent conversations or tool results.
Layer 2: Tool Execution & Runtime Sandboxing
Control 6: Enforce deterministic Pydantic/Zod schema validation on every tool argument. Control 7: Run code execution tools inside ephemeral microVMs with dropped Linux privileges.
Control 8: Ban dynamic `eval()`, `exec()`, or unparameterized SQL concatenation completely. Control 9: Establish hard step-count limits (e.g., maximum 20 iterative tool calls per session) to thwart Denial of Wallet recursion loops.
Control 10: Require Human-in-the-Loop (HITL) cryptographic approval for all irreversible or high-impact state modifications.
Layer 3: Network, Memory & Audit Logging
Control 11: Restrict outbound network egress using strict DNS domain whitelists. Control 12: Sanitize long-term vector embeddings against memory poisoning exploits.
Control 13: Mask all personally identifiable information (PII) and secret credentials before transmitting telemetry to third-party model providers. Control 14: Implement continuous audit logging of all intermediate tool arguments and raw LLM reasoning traces.
Control 15: Integrate automated adversarial red teaming into continuous delivery pipelines using frameworks like Garak and PyRIT.
AI Agent Security Checklist: Architecture & Technical Specifications Matrix
15 Production Security Controls Summary & Verification Audit Checklist:
| Layer | Control Name | Enforcement Mechanism | Verification Test |
|---|---|---|---|
| Input | 1. Dual-LLM Quarantine | Separate non-privileged extractor model | Adversarial prompt injection test |
| Input | 2. Token Delimiters | Cryptographic boundary XML tokens | Prompt boundary escape simulation |
| Input | 3. Payload Sanitization | Pre-parsing regex & length quotas | Buffer overflow & large payload test |
| Execution | 4. Schema Validation | Pydantic/Zod deterministic type checking | Fuzz testing function call arguments |
| Execution | 5. MicroVM Sandboxing | gVisor or Firecracker ephemeral containers | Container escape & root exploit test |
| Execution | 6. Step Counters | Hard limit on recursive reasoning loops | Infinite recursion simulation |
| Network | 7. Egress Firewall | Default-deny network security groups | Data exfiltration DNS/HTTP probe |
| Governance | 8. Human Approval (HITL) | Cryptographic signed webhooks for state edits | Simulated unauthorized transaction trigger |
Official Specifications & Primary Sources
Architectural specifications, model capabilities, and benchmark evaluations in this guide are cited from official documentation and published papers (verified as of October 2026):
- OWASP: OWASP Top 10 for Large Language Model Applications
- NIST: NIST Trustworthy and Responsible AI Standards
AI Agent Security Checklist: Engineering Questions & Practical Considerations
What is the most critical control on the checklist?
The Dual-LLM Quarantine pattern combined with MicroVM Sandboxing, because together they neutralize over 90% of all real-world prompt injection and tool hijacking attempts.
How can teams automate agent security testing in CI/CD?
By integrating open-source frameworks like Garak or PyRIT into GitHub Actions, executing automated adversarial fuzzing suites against model endpoints on every pull request.
Does sandboxing slow down agent response times?
Modern microVMs like AWS Firecracker and gVisor boot in under 5 milliseconds, adding virtually zero noticeable latency to agent execution workflows.
Join Our Official WhatsApp Channel
Get instant notifications for breaking AI developments, developer security guides, and tech intelligence directly on WhatsApp.
Recommended Reading